Skip to content

Wordfence

Wordfence blogundan derlenen guvenlik yazilarinin ozetleri.

Wordfence

Inside a Malicious, Stealthy WordPress Must Use Plugin

The Wordfence Threat Intelligence Team identified an interesting malware sample in mid June during a site clean. TThe malware was installed as a must-use plugin with several self-healing mechanisms in place in order to survive removal

via Wordfence

Wordfence

Wordfence Intelligence Weekly WordPress Vulnerability Report (September 7, 2026 to September 13, 2026)

Last week, there were disclosed in that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Security last week. Review those vulnerabilities in this report now to ensure your site is not affected. Our mission with Wordfence Intelligence is to make valuable vulnerability information easily accessible to everyone, ...Read More

via Wordfence

Wordfence

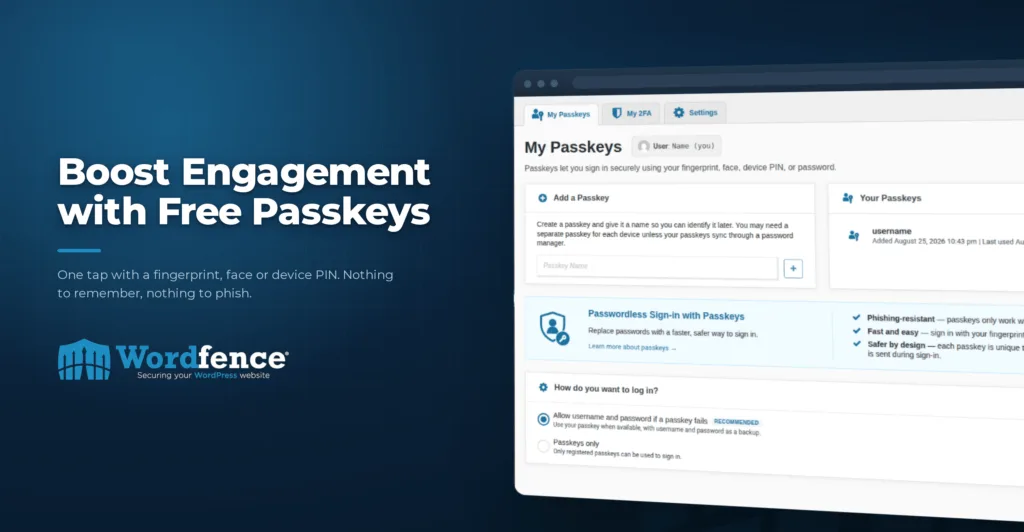
Boost Engagement with Free Passkeys by Wordfence

Wordfence 9 introduces passkeys, and passkeys provide a huge friction reduction because your user no longer has to remember their password or retrieve it from a password manager and copy/paste.

via Wordfence

Wordfence

Attackers Actively Exploiting Critical Vulnerability in WooCommerce Wholesale Lead Capture Plugin

On February 20th, 2026, a critical Unauthenticated Arbitrary File Upload vulnerability was publicly disclosed in WooCommerce Wholesale Lead Capture, a premium WordPress plugin with an estimated 6,000 active installations. This vulnerability can be leveraged by unauthenticated attackers to upload arbitrary files, including PHP backdoors, and achieve remote code execution.

via Wordfence

Wordfence

Wordfence Argus Identifies Two Critical Unauthenticated Vulnerability Chains Leading to Remote Code Execution in The Events Calendar Plugin

On August 21 and August 22, 2026, Wordfence Argus, created by the Wordfence Threat Intelligence team, identified two independent critical vulnerability chains in The Events Calendar, a WordPress plugin active on more than 600,000 websites. Both chains begin in the plugin's widget-rendering pipeline and can ultimately lead to Remote Code Execution without authentication through two separate methods.

via Wordfence

Wordfence

Wordfence Bug Bounty Program Monthly Report – May 2026

In May 2026, the Wordfence Bug Bounty Program received 1095 vulnerability submissions from our growing community of security researchers working to improve the overall security posture of the WordPress ecosystem. These submissions are reviewed, triaged, and processed by the Wordfence Threat Intelligence team, with validated vulnerabilities responsibly disclosed to vendors, often through the Wordfence Vulnerability ...Read More

via Wordfence

WordPress maintenance notes, once or twice a month

Backup, security and update practices for people who look after more than one WordPress site. No sales emails, unsubscribe in one click.

We send you a confirmation email first. Your address is only used for this newsletter — see our privacy policy.