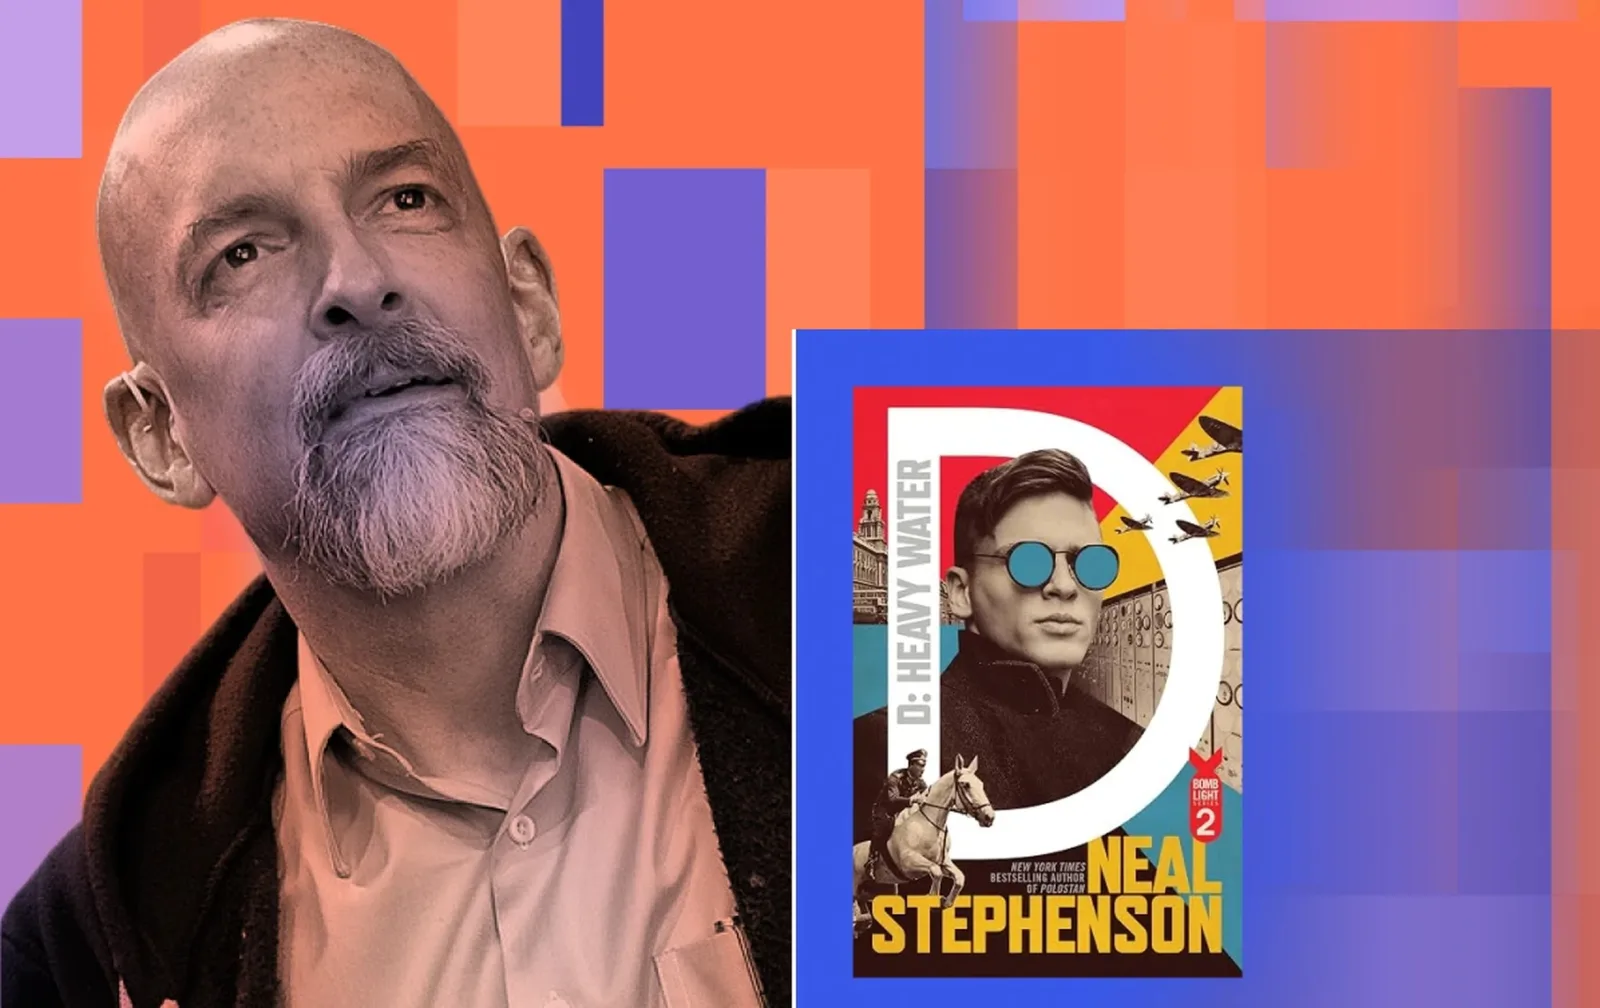
When Technology Outruns Its Institutions: Neal Stephenson on AI, Truth, and Control
Technology, truth, and the freedom to shape the tools we use. Neal Stephenson joins Zander Rose for the first Wide Margins conversation.
Practical maintenance, backup and security notes for agencies and freelancers managing many WordPress sites.
Technology, truth, and the freedom to shape the tools we use. Neal Stephenson joins Zander Rose for the first Wide Margins conversation.
TL;DR: WordPress 7.1.4 was released on October 28, 2026. According to WordPress, it includes fixes for 22 security vulnerabilities. The most serious is an unauthenticated race condition in the Core update process that can lead to remote code execution. Threat actors are already actively attempting to exploit it, so site owners should verify that WordPress ...Read More
In July 2026, the Wordfence Bug Bounty Program received 1077 vulnerability submissions from our growing community of security researchers working to improve the overall security posture of the WordPress ecosystem. These submissions are reviewed, triaged, and processed by the Wordfence Threat Intelligence team, with validated vulnerabilities responsibly disclosed to vendors, often through the Wordfence Vulnerability ...Read More
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Security last week. Review those vulnerabilities in this report now to ensure your site is not affected. Our mission with Wordfence Intelligence is to make valuable vulnerability information easily accessible to ...Read More
As of October 28, 2026, Wordfence knows of no WordPress site compromised through PHP2Shell. Update PHP to a fixed version and restart it, because updating WordPress does not update PHP.
The Wordfence Threat Response Team is a new small, technically hands-on team responsible for turning rapidly emerging threats into customer protection and clear customer guidance. Spot an active threat? Report it directly to threat-response@wordfence.com
Last week, there were disclosed in and that have been added to the Wordfence Intelligence Vulnerability Database, and there were that contributed to WordPress Security last week. Review those vulnerabilities in this report now to ensure your site is not affected. Our mission with Wordfence Intelligence is to make valuable vulnerability information easily accessible to ...Read More
On October 21st, 2026, the PHP project released emergency updates for two critical vulnerabilities tracked as CVE-2026-109618 and CVE-2026-109619. We warned site owners before the fixes became available and followed up after our team reviewed the vulnerability details and began testing the patched and vulnerable PHP releases. At this time, we have not observed any confirmed compromises resulting from these vulnerabilities, which is a clear indicator of this exploit's complexity considering…
Two critical PHP flaws, CVE-2026-109618 and CVE-2026-109619, can allow unauthenticated code execution. Updating WordPress won't fix them. Update and restart PHP.
Backup, security and update practices for people who look after more than one WordPress site. No sales emails, unsubscribe in one click.