Critical PHP Vulnerabilities (CVE-2026-109618 / 109619): What WordPress Site Owners Must Do
PHP's October 21, 2026 announcement covers two critical RCE flaws that also matter for WordPress sites. Which version to update to and what to do now.
Practical maintenance, backup and security notes for agencies and freelancers managing many WordPress sites.
PHP's October 21, 2026 announcement covers two critical RCE flaws that also matter for WordPress sites. Which version to update to and what to do now.
Two critical PHP vulnerabilities were disclosed on October 21, 2026. WordPress.com sites are already protected, with no action required from site owners.
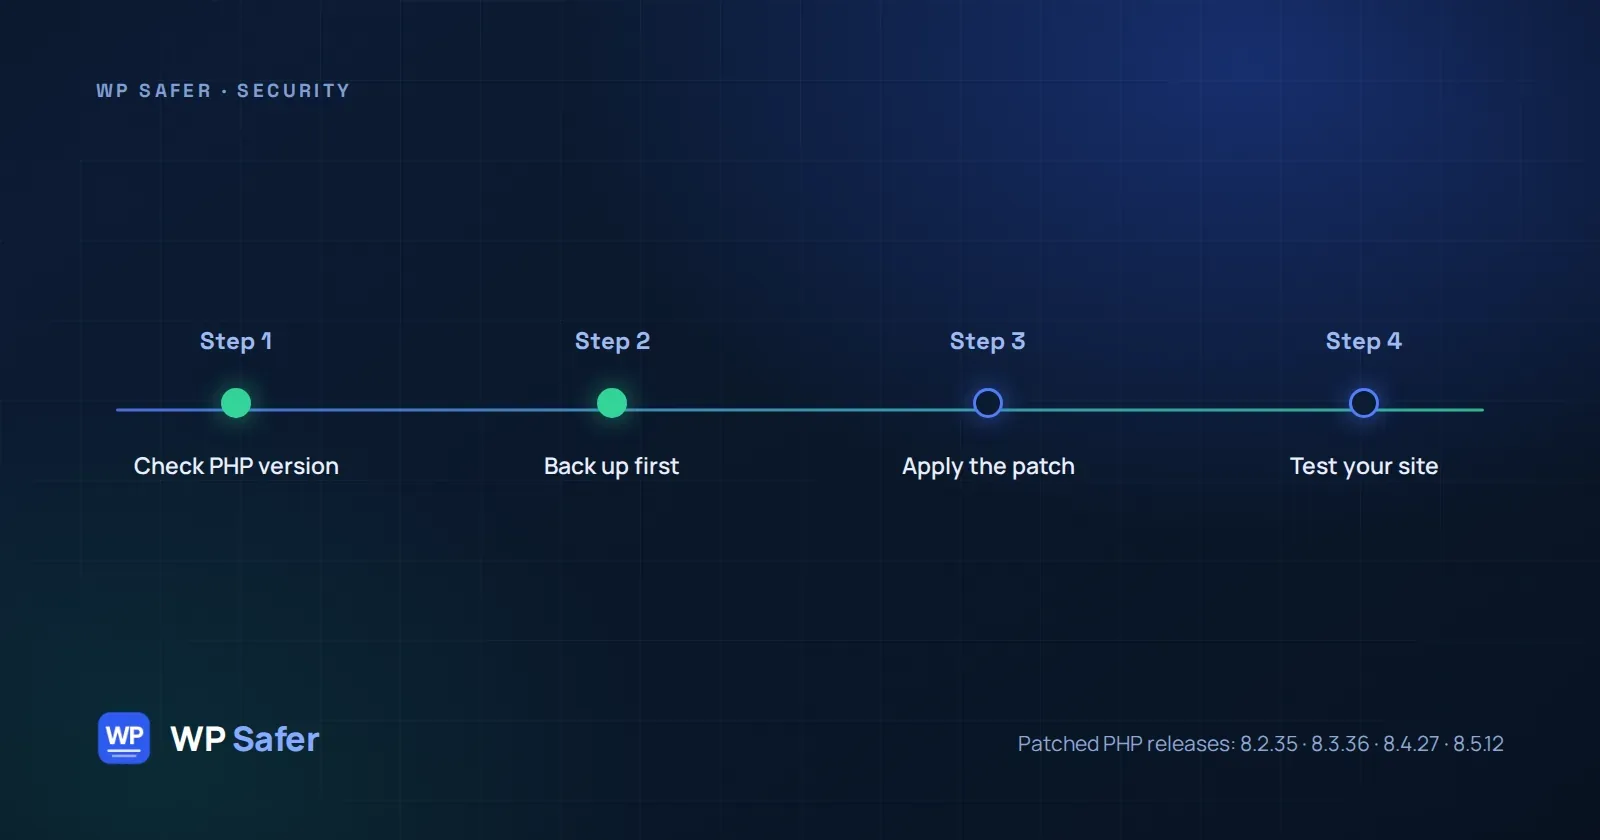
The PHP project has released PHP 8.5.12, 8.4.27, 8.3.36, and 8.2.35 to fix two critical vulnerabilities, CVE-2026-109618 and CVE-2026-109619, that can allow unauthenticated remote code execution. We recommend making sure every site you manage is running a patched version of PHP as soon as possible.
The PHP security team has issued advance notice of an upcoming critical security release, scheduled for Wednesday, October 21, 2026 at 14:00 UTC (10:00 AM Eastern). The release fixes two critical vulnerabilities, both rated 9.2 on the CVSS v4.0 scale. PHP is the programming language WordPress is built on. Every WordPress site runs on a ...Read More
Wordfence Argus helped uncover CVE-2026-82814, a high-severity unauthenticated PHP object injection in Duplicator and Duplicator Pro. Update to version 5.0.0 or newer.
TeamUpdraft has disclosed unauthorized access to its teamupdraft.com website over the weekend of October 17-18, 2026. The company believes its customer database was accessed and says that database contained connection keys for UpdraftCentral, UpdraftVault, and UpdraftClone, along with customer account information.
Rank Math has disclosed that some copies of Rank Math SEO PRO version 3.0.123 contained malware. According to Rank Math, the affected version was downloaded or installed through an update between October 15, 2026 at 20:02 UTC and October 16, 2026 at 07:12 UTC. If an affected copy of Rank Math SEO PRO 3.0.123 was ...Read More
Last week, there were 655 vulnerabilities disclosed in 406 WordPress Plugins and 100 WordPress Themes that have been added to the Wordfence Intelligence Vulnerability Database, and there were 236 Vulnerability Researchers that contributed to WordPress Security last week.
On September 17th, 2026, we received a submission for a Second-Order SQL Injection vulnerability in Backuply, a WordPress plugin with more than 600,000 active installations. This vulnerability makes it possible for authenticated attackers with subscriber-level access and above to store a malicious SQL payload that is executed when an administrator later restores a database backup, ultimately allowing the attacker to escalate their privileges to administrator and take over the site.
Backup, security and update practices for people who look after more than one WordPress site. No sales emails, unsubscribe in one click.